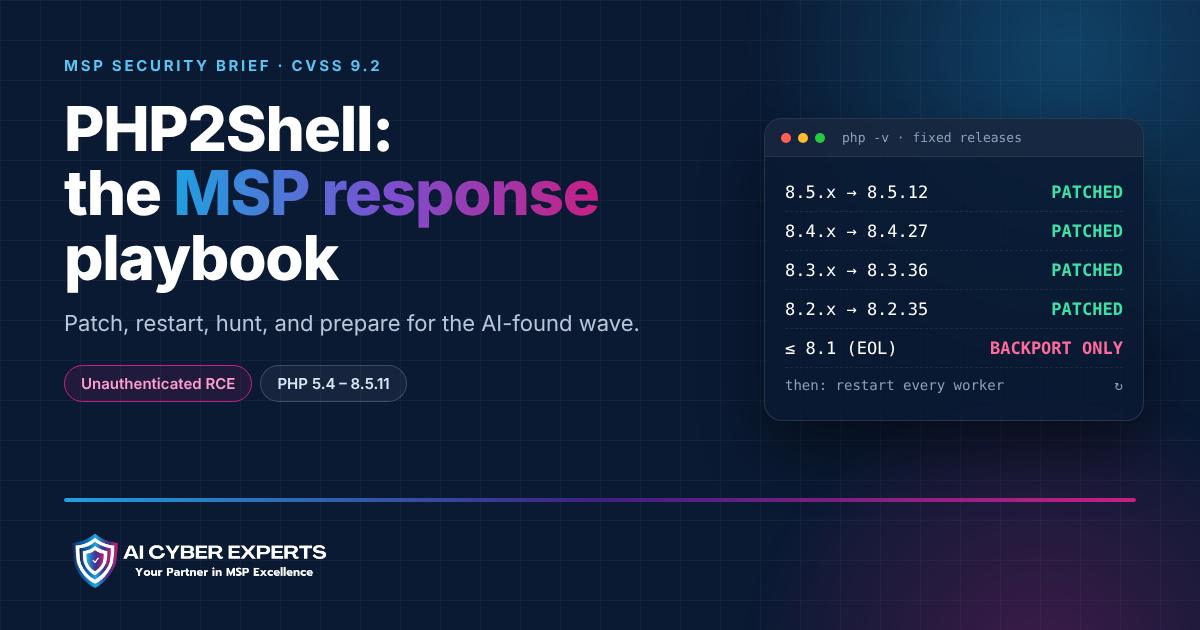
On 21 October 2026, PHP shipped emergency fixes for PHP2Shell: two critical flaws that let an unauthenticated attacker run code on a web server before any application or login runs. Every PHP release from 5.4 to 8.5.11 is affected. If your clients have websites, portals, WordPress, or any line-of-business web app, you have exposure. This is the response plan we'd run across a client base this week, followed by the bigger lesson: PHP2Shell is only the first wave of memory-corruption exploitation going mainstream.
· October 23, 2026
Read the guide